


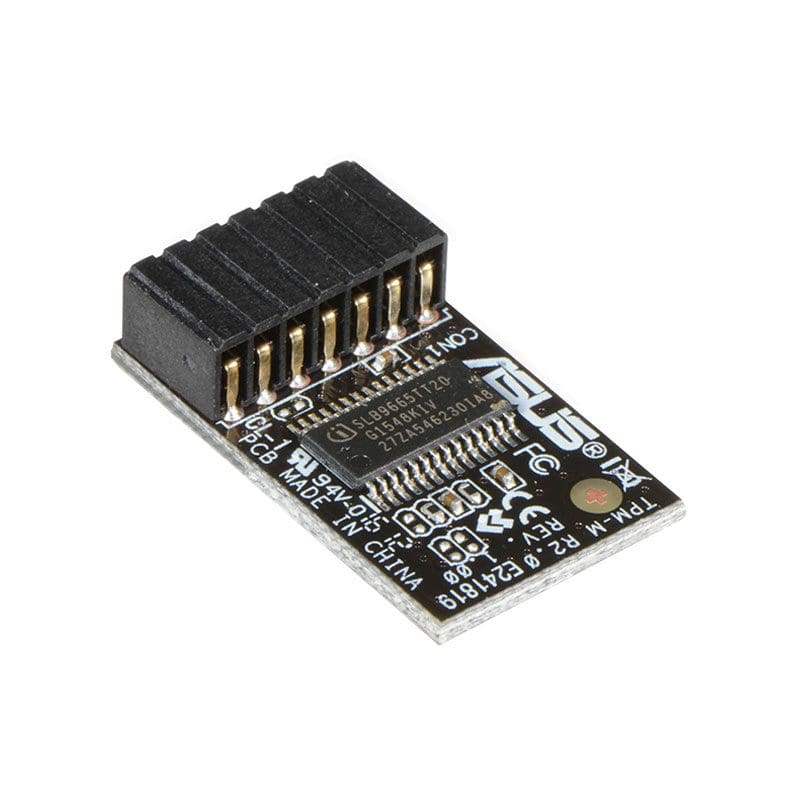
TPM‑M Specifications
Trusted Platform Module (TPM) for Enterprise Security
Manufacturer: Generic / TPM Module OEM
Manufacturer Model: TPM‑M
Product Line: TPM Security Module
Product Series: TPM‑M
Product Type: Hardware Security Module (TPM)
Product Name: TPM‑M Trusted Platform Module
KEY FEATURES:
Provides hardware-based security functions
Supports secure generation and storage of cryptographic keys
Enhances platform integrity and system authentication
Compatible with TPM 2.0 standard
Enables secure boot and measured boot
Supports full disk encryption solutions (BitLocker, etc.)
PERFORMANCE:
Cryptographic Functions: RSA, ECC, SHA-1, SHA-256, HMAC, Key Generation
Key Storage: Secure non-volatile memory
Platform Attestation: Supported
Random Number Generator: Hardware-based true RNG
ENVIRONMENTAL & RELIABILITY:
Operating Temperature: Typical ambient server/PC conditions
Designed for continuous operation in enterprise systems
Complies with TCG (Trusted Computing Group) specifications
PHYSICAL:
Form Factor: Mini PCIe / Module (varies by vendor)
Typical Dimensions: Small module suitable for motherboard TPM header
Weight: Negligible (<0.05 lb / 25 g)
Reviews
There are no reviews yet.